Third-Party Risk Management
Why Current TPRM Does Not Cut It
Risk evaluation is largely point-in-time — a snapshot at onboarding and periodic reassessments, not an ongoing view.
Fragmented and inefficient processes — spreadsheets, email and manual evidence collection with inconsistent visibility.
Programs stop short of the vendor full lifecycle — centered on due diligence, onboarding and periodic reassessments, without post-onboarding governance, contract compliance, continuous monitoring, remediation and offboarding.
Inadequate coverage of the extended supply chain — fourth and fifth parties behind direct third parties are difficult to identify and monitor.
Enlighta is TPRM using automation and AI across the third-party lifecycle — extending beyond initial assessment and onboarding into the full vendor lifecycle, with automation, external intelligence and AI-assisted workflows.
What Does Enlighta Cover Across the Third-Party Lifecycle?
From prospective vendor screening through onboarding, contractual governance, continuous monitoring and offboarding — with risk continuously visible to management. Explore the Enlighta TPRM lifecycle and drill into selected capabilities.
Enlighta’s TPRM Solution Platform
The lifecycle continues through post-onboarding governance, contract compliance, continuous monitoring and remediation — to eventual vendor offboarding: transition planning, data return or destruction, outstanding obligations, access termination and closure of remediation items.
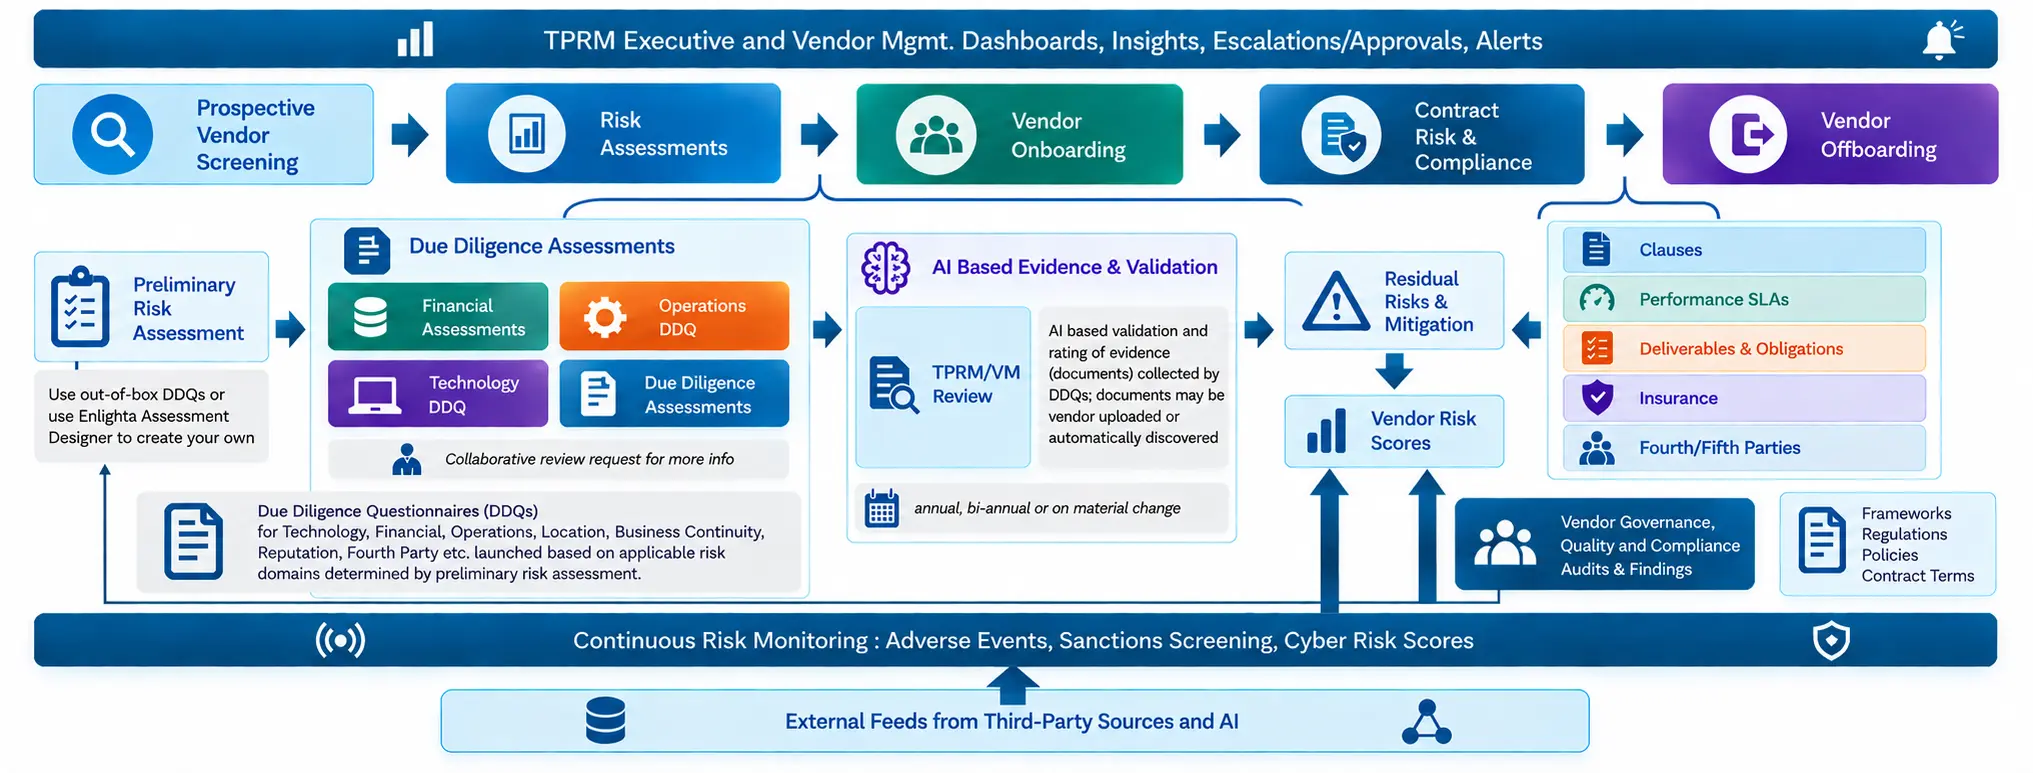
TPRM Executive and Vendor Mgmt. Dashboards, Insights, Escalations/Approvals, Alerts
Know Who You Are Onboarding
Vendor context, criticality and external screening — consolidated before any assessment begins.
Noventra Systems
Critical Third PartySCREENING RESULT
Establish the Risk Context First
A short structured assessment determines inherent risk — criticality and materiality — before any due-diligence questionnaire is sent.
Preliminary Risk Assessment — Noventra Systems
DraftThird-Party Context
Criticality / Materiality
The Preliminary Assessment Drives the Next Assessments
Applicable risk domains and their basis are determined automatically. Launch the required due-diligence assessments.
| Risk Domain | Applicability | Basis | Action |
|---|---|---|---|
| Information Security | Required | Sensitive data access | |
| Privacy | Required | Personal data processing | |
| Business Continuity | Required | Critical service | |
| Financial Viability | Required | Material dependency | |
| Compliance | Required | Regulatory exposure | |
| Reputation & ESG | Conditional | Engagement profile | Review |
| People Competency | Not Required | Low dependency | — |
| Subcontractor Management | Required | Fourth-party dependency |
Risk Domain Evaluation — informed by
Example — Financial Viability
Informed through assessment questions as well as external financial intelligence — not questionnaires alone.
Create or Adapt Risk Assessments
Configure how questions, domains, weights and applicability rules determine due-diligence requirements.
Third-Party Information Security Assessment · Domain Assessment · Applicable Risk Domain: Information Security
Question → Risk Domain Mapping
| Question | Risk Domain | Weight | Req. |
|---|---|---|---|
| Does the supplier encrypt sensitive data? | Information Security | 10% | |
| Is MFA enforced? | Information Security | 10% | |
| Is there an incident response plan? | Operational / InfoSec | 15% |
Applicability Rules — Automated Due Diligence
Each Risk Domain Has Its Own Assessment
Assessments run in parallel with their own status pipeline. Switch between domain assessments.
Information Security Assessment — Noventra Systems
Vendor RespondingQuestions
Assessment Facts
TPRM, Business, Risk & Compliance and the Supplier — One Workflow
Assessment inputs, questionnaires, documents, clarification and remediation all move through one collaborative assessment. Click an activity to follow it.
Activity
Participants
Workflow
Documents, Responses and Supporting Evidence in One Place
Evidence collected through the assessment, with automated and manual collection. Click any item to inspect it.
Vendor Onboarding — document collection and validation sit inside the onboarding gate, separate from Risk Assessments.
Information_Security_Policy.pdf
PolicyAutomated Validation — Findings, Missing Controls and AI Responses
AI validates supplier evidence and surfaces gaps for reviewer action. Review the finding and choose a reviewer action.
Information_Security_Policy.pdf
AI Review RunningAI Validation
Vulnerability management evidence was not identified.
AI Response
Analyzing documentEvidence supports the presence of an information-security policy but does not establish sufficient evidence of vulnerability-management controls.
Reviewer Actions
AI Assists. Humans Review and Approve.
Manual review is explicit, and approval stays with the accountable reviewer.
Review Context
Reviewer Controls
Decision
Assessment Approved — Manual Approval Recorded
ApprovedAutomate the analysis. Keep the decision with the accountable reviewer — TPRM and functional stakeholders remain accountable for risk decisions.
Assessment Outcomes Across Risk Domains
Domain scores roll up into the third-party risk scorecard — initial risk, mitigation and residual risk.
Third-Party Risk Scorecard — Noventra Systems
Overall Risk: Moderate| Risk Domain | Score | Status | Trend |
|---|---|---|---|
| Information Security | 72 | Moderate | |
| Privacy | 81 | High | |
| Business Continuity | 64 | Moderate | |
| Financial Viability | 88 | High | |
| Compliance | 76 | Moderate | |
| Reputation & ESG | 91 | High |
Risk Domains
External intelligence feeds risk domains directly — a signal can change a domain score or status without a new questionnaire. Click a feed.
Risk is dynamic. Assessments and DDQs are point-in-time — adverse events, sanctions, cyber risk, geographic events and fourth/fifth-party changes are monitored continuously. Identify Risk Signals using Continuous Monitoring.
External Intelligence → Risk Evaluation
External ratings and data inform risk domains and scores.
External Intelligence → Continuous Monitoring
External feeds generate ongoing monitoring signals.
Assessment Establishes the Baseline. Monitoring Identifies Change.
Continuous monitoring watches every third party after approval — and feeds change back into the risk lifecycle. Simulate a new signal.
Monitoring Scope
The Continuous TPRM Loop
A Risk Signal Triggers an Updated Assessment
The cyber rating drop touched the Information Security risk domain — initiate the reassessment to update the risk picture.
REASSESSMENT TRIGGERS — annual, bi-annual or on material change
Cyber security rating decreased 78 → 61 · Impact: Information Security risk domain · Domain status: Reassessment Required
Information Security — Reassessment
Vendor RespondingScore Impact
From Risk Assessment to Risk Mitigation
A risk identified through the risk assessment, recorded in the Risk Register, reflected in Risk Scorecards, with a mitigation action — and continuously monitored.
| Risk | Risk Domain | Register Entry | Scorecard | Mitigation / Action | Monitoring |
|---|---|---|---|---|---|
| Backup restoration not demonstrated | Operational | Registered | BC score 64 · Moderate | Quarterly DR test + evidence | Monitored |
| Vulnerability management gap | Information Security | Registered | InfoSec score 72 · Moderate | Updated VM program + scan evidence | Monitored |
| Regional regulatory exposure | Compliance / Geopolitical | Registered | Compliance score 76 · Moderate | Local counsel review | Monitored |
Actual Events Become Tracked, Owned Actions
Actual events — SLA breaches, audit findings, control failures, compliance gaps, contractual breaches and incidents — are tracked to remediation. Raise one now.
Risk Issue
High OpenAction
Awaiting VendorVendor Security Manager · due 15 Oct 2026
Action Path
- Request updated remediation plan
- Initiate reassessment
- Monitor evidence
- Escalate if unresolved
Capture Contractual Requirements — Monitor the Commitments
Capture contractual requirements and monitor whether contractual commitments are being met — part of the ongoing vendor lifecycle, not a standalone endpoint. Click a component.
| Vendor | Contract | Obligation | Due Date | SLA | Status |
|---|---|---|---|---|---|
| Noventra Systems | MSA-2026-04 | Quarterly DR test evidence | 30 Sep 2026 | 99.9% availability | On Track |
| Noventra Systems | MSA-2026-04 | Incident notification within 24h | Ongoing | Security SLA | Met |
| Noventra Systems | DPA-2026-11 | Annual penetration test | 15 Dec 2026 | Security clause | Due Soon |
Vendor Governance, Quality and Compliance Audits & Findings
Audits run against frameworks, regulations, policies and contract terms. Each finding drives corrective action — with risk impact or an Issue only where applicable. Click an audit.
An audit finding remains a finding — it is not itself a risk. Where it creates exposure or an actual gap, it flows to Risk Impact or an Issue.
SOC 2 Type II — Surveillance Audit
Against framework: SOC 2 Trust Services CriteriaOne Dashboard Suite for the Whole TPRM Program
Management visibility across every layer of the operating model. Open a dashboard — most are live in this demo.
Enterprise-Wide Third-Party Risk Posture
The management layer from the process map, in one view — posture, trends, escalations and approvals.
Risk Distribution — High / Medium / Low
Risk Distribution & Initial vs Residual
Top-Risk Vendors & Escalations
Who Are the Third Parties — and Where Do They Stand?
The vendor inventory is the foundation for every other dashboard. Click a vendor row.
| Vendor | Category | Criticality | Business Owner | Risk | Assessment | Contract | Monitoring |
|---|---|---|---|---|---|---|---|
| Noventra Systems | Technology | Critical | VP Operations | Moderate | Approved | Active | Live |
| CloudLine Hosting | Infrastructure | High | Head of IT | Moderate | Vendor Responding | Active | Live |
| Meridian Logistics | Logistics | High | COO Office | Low | Internal Review | Renewal Due | Live |
| PayBridge Services | Payments | Critical | CFO Office | High | Reassessment Required | Active | Live |
| GreenFields Facilities | Facilities | Medium | Facilities Lead | Low | Not Required | Active | Live |
Book a Personalised Demo Today
Walk the complete TPRM operating model with your own vendors, risk domains and governance structure.
Ready to see it on your data?
A guided session with a product specialist — your use cases, your risk domains, your questions answered.