Enlighta GovernAI — Enterprise AI Governance
Know It. Govern It. Enforce It.
From model inventory to runtime enforcement, across every team and vendor.
AI-Related Breaches Are Real, Costly and Growing
Verified figures from IBM’s 2026 Cost of a Data Breach study covering 602 organizations.
Source: IBM 2026 Cost of a Data Breach
Different Jurisdictions. Different Obligations. One Governance Challenge.
Concrete regulatory examples — not a generic “regulation is increasing” claim.
Real-world liability — Air Canada chatbot: A Canadian tribunal held Air Canada responsible for inaccurate information supplied by its website chatbot, illustrating that organizations remain accountable for AI-generated customer-facing information. (Moffatt v. Air Canada)
AI Adoption Has Outpaced the Controls Built to Govern It
AI models, vendors, agentic workflows, data sources, policies and business intent — with fragmented governance, disconnected teams, incomplete enforcement and incomplete auditability. Click any element to continue.
Five Master Stages. One Connected Process.
Every screen in this demo belongs to one of these five stages.
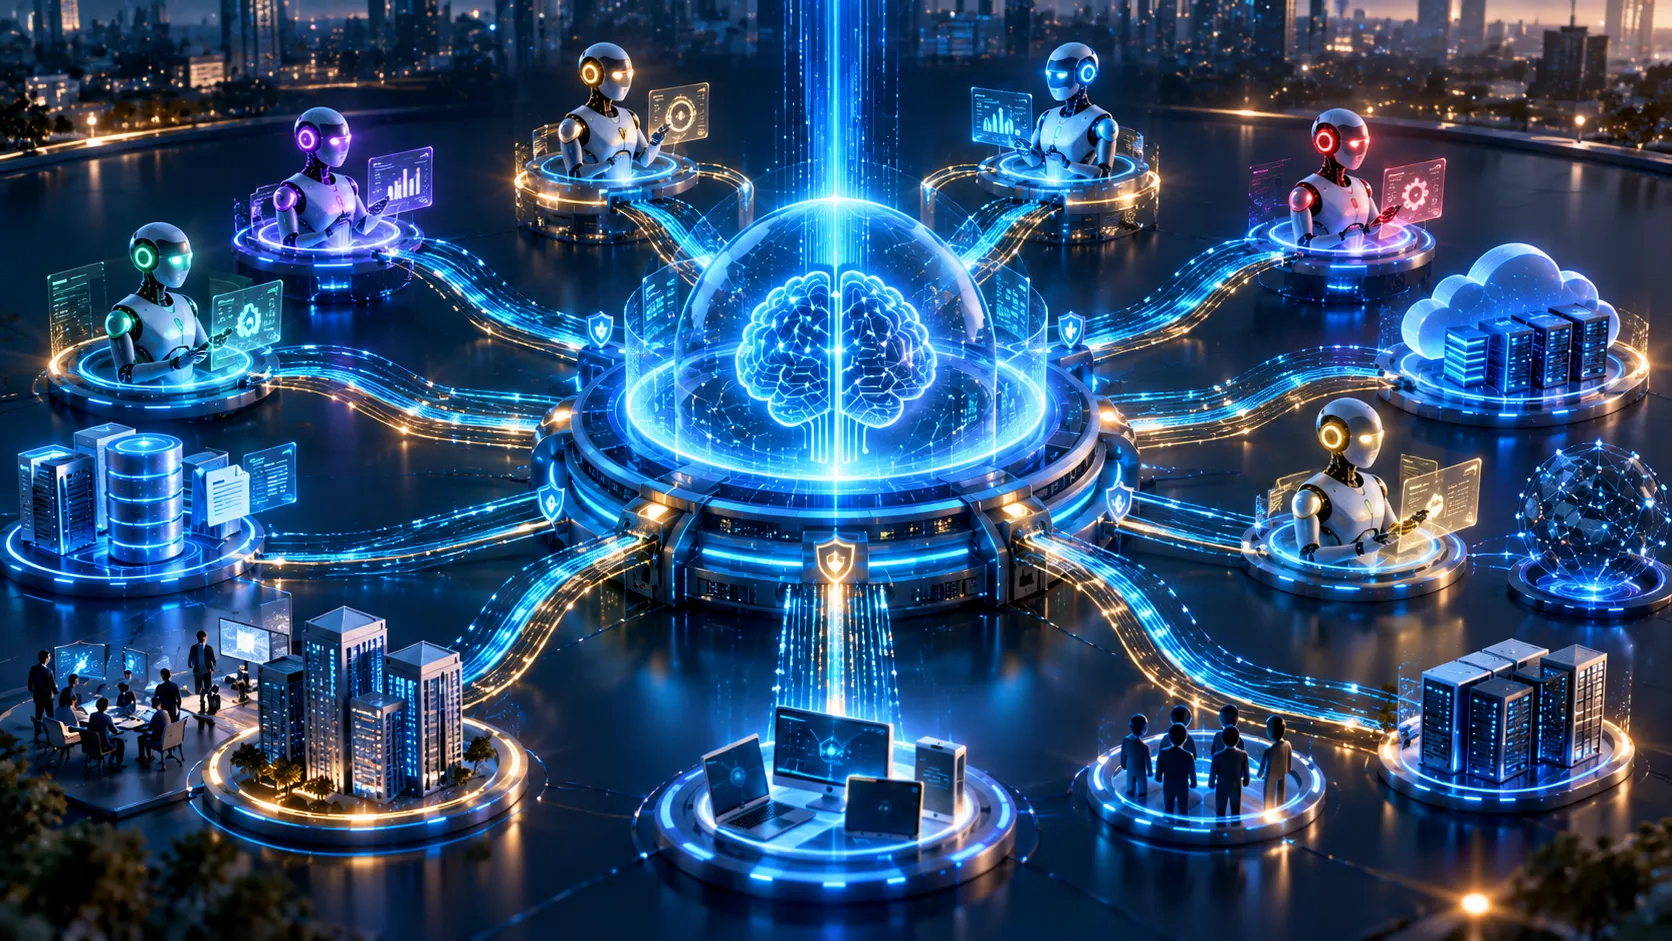
A Connected Ecosystem of AI Agents
Multiple agents. Different purposes. Different data. Different risks.
You Cannot Govern What You Cannot See
A centralized, searchable, continuously maintained inventory of AI assets — internal and vendor-deployed, including unsanctioned AI.
Enterprise Contract Assistant
A complete governance record — purpose, approved and restricted use, data, dependencies, owners and policies.
Concrete AI Security Threats
Three risks the wireframe calls out — and how the inventory connects to runtime controls and vendor oversight.
Malicious instructions embedded in prompts or documents can cause unintended model behavior or downstream actions.
Repeated querying can expose fragments of sensitive information embedded in model training.
Unsanctioned AI tools can cause confidential information to leave the organization's controlled environment without governance or audit trail.
Data & Privacy
PII and protected-section detection, redaction and blocking at the API proxy layer — with full audit logging.
The Authoritative Governance Repository
Policies, SOPs, controls and guardrails — searchable, revisable and linked to the models they govern.
Define What the AI Is Allowed to Do
Purpose and permitted use are the foundation for runtime policies. Click any row.
Accounts Receivable AI Agent — HIPAA-Aligned Governance Scenario
Help the AR team identify patients with outstanding payments and recommend payment-plan or deferred-payment options.
Claims / Fraud AI Agent
AI agents can summarize claim histories or estimate repair costs from photos — GovernAI ensures the agent stays within its purpose.
Risk scenario: an AI agent used to identify an auto-approval threshold for claims, creating potential fraudulent-claim exposure. GovernAI’s intent boundaries and post-runtime analysis detect and flag this.
Structured Sign-Off Across Teams
InfoSec, Privacy, Legal, HR, Procurement, Compliance — and where applicable, external vendors.
Preventing AI From Doing What It Should Not
Three safety concerns — and the GovernAI response.
An AI system begins performing tasks beyond its approved purpose.
An AI agent can take sequences of actions across multiple systems.
A vendor's model can change capabilities without adequate visibility.
Periodic and Ad Hoc Assessments
For internal AI and vendor AI — with alignment areas, not certification claims.
Assessment Workspace
Every assessment connects the model, vendor, purpose, risk dimensions and framework — with findings and mitigations.
Make Sure AI Performs as Expected
Four drift risks — and the GovernAI controls that address them.
Ongoing Compliance & Performance Metrics
When a significant change or anomaly occurs, an ad hoc reassessment is triggered.
Dependencies, Validation and Response
A model's dependencies and responsible stakeholders are visible as part of the governance record.
Human review checkpoints on designated high-risk outputs before they are acted on.
Incident notification stakeholders are pre-linked to the model record.
Contractual Guardrails for AI
Indemnification · Audit Rights · SLAs · Data Privacy · Purpose / Intent Scope.
“The model may use data only for the defined target purpose.”
Know Who Is Responsible
Who approved this model, who owns it, who operates it, and who must respond when something changes?
GovernAI Enforce
Governance at the point of use — not just on paper. Runtime enforcement intercepts requests before they reach the model.
AI Usage Governance Control Plane
Machine-readable policy evaluation, intent inference, sidecar enforcement, audit trail and telemetry.
Detection · Redaction · Blocking · Logging
Four control types applied at runtime. Click each to continue.
“Summarize the delivery terms for the contract signed by Jane Smith (PII)…”
Runtime Scenario — Out-of-Scope Request
“Extract pricing structures and competitor clauses from this contract.”
Review Required for High-Risk Decisions
Configurable human review checkpoints for designated high-risk use cases — inside Enforce at Runtime.
AI Incidents, Tracked to Resolution
Escalation, root cause analysis, corrective actions, incident tracking and a full audit trail.
Incident: Out-of-Scope AI Request
Blocked Under Review AI-2026-014
Incident RCA & Corrective Action
Within Respond to Incidents — RCA and corrective-action tracking through resolution.
AI Usage Log Analysis
Even when a request is not blocked at runtime, GovernAI analyzes the interaction afterward to identify what happened and what was unexpected.
Every Interaction Linked to Policy and Intent
Runtime controls generate the audit evidence needed to demonstrate governance.
Monitoring Dashboard
An outcome and monitoring view — not a detection lifecycle.
Bias, Fairness, Transparency and Disclosure
Periodic and ad hoc bias/fairness assessments, regulatory alignment and documentation — governance requirements covered by the source.
Approved AI vs Unsanctioned AI
Continuous inventory visibility includes unsanctioned tools — AI inventory is broader than registered enterprise models.
Third-Party AI Governance
Do you know all AI agents/models used by third parties, what data they may use, applicable policies — and whether responses stayed within intended function?
Vendor Changes Its AI Model Configuration
Security teams are alerted when vendor AI configurations change.
Vendor AI Sales Portal Agent — Prompt Injection Attempt
A vendor AI agent helps brokers manage their book of business. Simulated demo scenario.
Sidecar for AI Models — Including Agentic AI & AI Code Gen
Audit trail and telemetry attached to every model interaction.
Connected Governance, Not Separate Workstreams
Each capability feeds the next — with vendor governance connected across the architecture.
Know It. Govern It. Enforce It.
TPRM · Performance Management · Obligations · Issues & Remediation