The Vendor Risk Management Process: Steps, Challenges, and Best Practices for 2026
A single compromised vendor can cost an organization millions in regulatory fines, lost revenue, and reputational damage, yet most procurement and risk leaders still cannot describe their own vendor risk management process end to end. Industry reporting consistently finds that the majority of data breaches now involve a third party, and IBM’s Cost of a Data Breach research has repeatedly shown that breaches involving vendors cost more and take longer to contain than internal-only incidents. The gap between knowing vendor risk is a problem and having a structured vendor risk management process to govern it is where most enterprises currently sit.
A working vendor risk management process is what separates organizations that govern vendor exposure deliberately from those that discover it during an audit or a breach disclosure call. When the vendor risk management process flow is well defined, every vendor moves through the same screening, assessment, contracting, monitoring, and offboarding stages with documented evidence at each step. When it isn’t, vendor risk lives in spreadsheets, point tools, and individual inboxes, and the gaps between them are exactly where vendor failures originate.
This guide covers what the vendor risk management process is, the key steps that make up the full vendor risk management process flow, examples of vendor risk worth knowing, the common challenges organizations face, the tools mature programs use, and best practices for closing the gaps that hurt most.
What Is the Vendor Risk Management Process?
The vendor risk management process is the end-to-end sequence of activities an organization uses to identify, assess, mitigate, and continuously monitor the risks introduced by its commercial vendors, suppliers, and service providers, from the moment a vendor is being evaluated through to the moment the relationship is fully closed out. It is the structured discipline that converts a vague awareness of vendor exposure into documented, repeatable, audit-ready governance.
Vendor risk management (VRM) is often discussed alongside third-party risk management (TPRM). The terms overlap heavily, but vendor risk management typically focuses on commercial vendors providing products or services, while TPRM is the broader umbrella covering vendors, suppliers, partners, brokers, contractors, and any external entity that interacts with your data, systems, customers, or operations. What both share is a structured process: a sequence of stages every vendor passes through, with evidence collected at each one.
In practical terms, the vendor risk management process answers three questions reliably for every vendor:
What could go wrong if this vendor fails, is breached, or behaves unethically?
How likely and how severe is that exposure today, and how is it changing?
What controls (contractual, technical, and operational) keep the risk inside our tolerance?
A modern vendor risk management process flow extends well beyond cybersecurity. A mature program assesses financial viability, operational resilience, regulatory and sanctions compliance, ESG exposure, concentration risk, geopolitical exposure, and even fourth- and fifth-party (sub-contractor) risk.
The purpose of a structured vendor risk management process is to keep external dependencies from becoming the weakest link in the enterprise. Several forces have moved the vendor risk management process from a back-office procurement task to a board-level concern:
Vendor portfolios have expanded dramatically. The average enterprise today engages thousands of vendors, each one effectively a new entry point into the business.
Regulatory scrutiny has intensified. Frameworks like the EU’s DORA, the U.S. Interagency Guidance on Third-Party Relationships, GDPR Article 28, India’s DPDP Act, and NYDFS Part 500 all hold the primary organization accountable for what its vendors do with data and systems.
Breach economics have shifted. Vendor-involved breaches consistently cost more and take longer to contain than internal-only ones.
Concentration risk is real. When entire industries depend on the same handful of cloud providers, SaaS platforms, or contract manufacturers, a single outage cascades.
Accountability cannot be outsourced. Customers, regulators, and shareholders hold the primary organization responsible, regardless of which vendor caused the failure.
A defined vendor risk management process is how organizations operationalize that accountability. Without it, vendor governance becomes reactive: problems surface when somebody happens to notice them, usually too late to act cheaply.
Examples of Vendor Risk
A vendor risk is any potential negative event arising from a vendor relationship. The categories worth knowing inside any vendor risk management process flow include:
Cybersecurity and data risk. A vendor with weak controls suffers a breach that exposes your customer data. The 2023 MOVEit Transfer breach is a textbook example: a single file-transfer vendor’s vulnerability affected thousands of downstream organizations.
Operational risk. A critical SaaS provider goes down and your customer-facing systems go with it.
Financial risk. A key supplier becomes insolvent, disrupting your supply chain or core operations.
Compliance risk. A vendor processes EU personal data without an adequate transfer mechanism, putting you in violation of GDPR.
Reputational risk. A contractor is caught using forced labor, and your brand is dragged into the story.
Sanctions and financial-crime risk. A new supplier turns out to be on a global sanctions list, exposing you to OFAC or equivalent penalties.
Concentration risk. Too many critical services are sourced from a single geography or single provider.
Fourth- and fifth-party risk. Your vendor outsources part of its work to someone you’ve never assessed.
AI risk. A vendor embeds generative AI into its product, and sensitive data flows into model training corpora without your visibility.
Each of these is a category the vendor risk management process needs to address. Programs that treat vendor risk as a cybersecurity-only problem miss the majority of where actual exposure now sits.
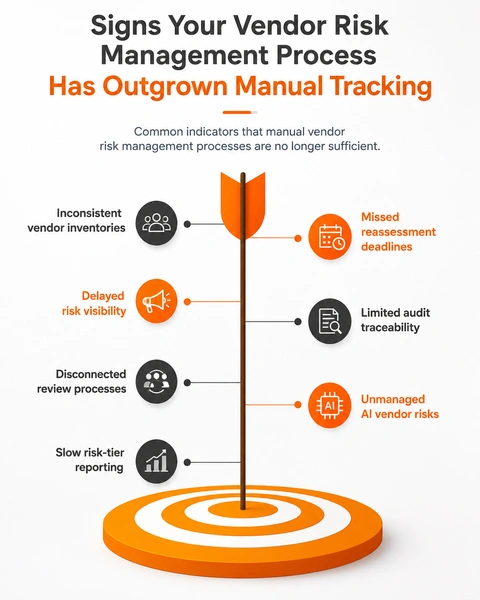
Signs Your Vendor Risk Management Process Has Outgrown Manual Tracking
Most organizations don’t decide to formalize their vendor risk management process in one deliberate moment. They drift into needing one while still relying on spreadsheets, email threads, and a shared drive. A few signals tend to appear first:
Different teams maintain different vendor inventories that don’t reconcile.
Reassessments slip past their due dates because no one is tracking them.
Adverse events about your vendors reach you through news headlines, not your own monitoring.
You can’t trace, for audit, when a specific vendor was last assessed or by whom.
Contracting and risk reviews happen in parallel and disagree at the end.
AI tools are entering your business through existing vendors and no one is governing them.
Producing a current, risk-tiered list of your top 50 vendors takes more than an hour.
If two or more of these feel familiar, the organization has likely already outgrown manual tracking. The only open question is how much that gap is currently costing in unmonitored risk.
The Vendor Risk Management Process Flow at a Glance
Different sources break the vendor risk management process into anywhere from 4 to 8 phases. What matters is that all of these activities are covered, not the exact count.
Below is each step expanded, with the activities and decisions that define a mature vendor risk management process flow.
Step 1: Identification, Screening, and Tiering
The vendor risk management process begins before a vendor is formally engaged. A business owner identifies a need, submits an intake request, and the vendor enters the screening pipeline.
Screening at this stage includes sanctions screening against global watchlists (UN, EU, DFAT, OFAC) and other law enforcement lists, PEP (Politically Exposed Person) screening, AML/CTF compliance verification, adverse media monitoring, and detection of 4th- and 5th-party relationships.
Once screening clears, vendors are tiered by criticality, typically into Tier 1 (high risk / mission-critical), Tier 2 (medium), and Tier 3 (low). Tiering determines how much scrutiny the rest of the vendor risk management process applies. Applying the same depth of assessment to every vendor wastes resources on low-risk relationships and under-assesses the ones that actually matter.
Step 2: Due Diligence and Risk Assessment
Once tiered, vendors move into due diligence. This is where the vendor risk management process examines whether the inherent risks identified during screening are matched by adequate controls.
Tier-appropriate due-diligence questionnaires (DDQs) are dispatched to the vendor and internal stakeholders, covering risk domains including information security and cyber risk, privacy, financial viability, operational competency, concentration, reputational risk, technology, sub-contractor exposure, financial crimes, anti-money laundering, human resources, background screening, and ESG.
Evidence is collected, validated, and scored. Initial and residual risk ratings are assigned, and the vendor risk management process advances only if residual risk falls within the organization’s appetite. If it doesn’t, the next step is either mitigation or walking away.
Step 3: Contracting and Risk Mitigation
Identified risks need to be translated into enforceable contractual controls. This stage of the vendor risk management process flow converts assessment findings into terms that survive the rest of the relationship: SLAs, data protection agreements, audit rights, right-to-terminate clauses, insurance requirements, sub-processor restrictions, and exit obligations.
Skipping or under-resourcing this step is common, especially when contract review happens in parallel to risk assessment rather than informed by it. When the two are connected, the contract reflects what the assessment surfaced. When they aren’t, the contract reflects whatever legal negotiated last time and the assessment findings sit in a separate report nobody opens during disputes.
Step 4: Onboarding and Vendor Information Management
With contracts signed, the vendor moves into operational onboarding. The vendor risk management process at this stage focuses on building a complete, structured vendor record: legal entities, hierarchies, sites, categories, products and services, key contacts, financial data, document repository, and 4th- and 5th-party relationships.
A self-service vendor portal can streamline onboarding. Vendors register, upload required documents (ownership documents, insurance certificates, attestations), and submit information directly into the platform rather than via email. AI-driven document extraction validates the uploaded information and flags discrepancies.
A clean onboarding record is what makes every later step in the vendor risk management process possible. Without it, monitoring becomes guesswork.
Step 5: Ongoing Monitoring and Performance Management
This is where most vendor risk management processes fail. Traditional approaches collect a thorough due diligence package at onboarding and then go silent until the next annual review. By then, the vendor’s risk profile may have changed completely.
A modern vendor risk management process includes continuous monitoring across:
Adverse Events Monitoring. AI-powered scanning of news sources such as The Wall Street Journal, Bloomberg, Associated Press, Reuters, and MSNBC, plus configurable feeds drawn from 10,000+ data sources, with auto-classification into risk domains like litigation, data breaches, and financial events.
Sanctions Monitoring. Continuous re-screening against global watchlists.
Financial Health. Ongoing review of credit ratings, going-concern indicators, and key financial metrics.
SLA and KPI Performance. Automated tracking of vendor performance against contractual commitments, with self-reporting through the vendor portal or integration with ITSM tools like ServiceNow.
Periodic reassessments are still scheduled (annually for Tier 1, less frequently for lower tiers), but they’re informed by what continuous monitoring has surfaced in between, not by what the vendor said about themselves twelve months ago.
Step 6: Governance and Issue Management
Monitoring surfaces signals. Governance is what the organization does with them.
This stage of the vendor risk management process flow includes Quarterly Business Reviews (QBRs), Strategic Business Reviews (SBRs), and VMO meetings with pre-populated agendas and tracked action items; issue and gap tracking with automated escalation rules; balanced scorecards combining performance, risk, and compliance metrics; vendor relationship health surveys covering alignment, performance, risk, compliance, quality, capabilities, and ESG; and action item assignment across internal teams and vendors.
Issues that aren’t tracked become disputes. Disputes that aren’t resolved become unscheduled terminations. The vendor risk management process at this stage is what prevents that escalation by surfacing problems early and routing them to the right people with documented evidence.
Step 7: Offboarding and Termination
The final step in the vendor risk management process is the one most often skipped. When a vendor relationship ends, structured offboarding ensures no residual exposure: automated offboarding checklists for IT, Data, Finance, HR, and Contracts; triggering contractual obligations such as Certificate of Data Destruction; revocation of system access; knowledge transfer documentation; and archive of historical vendor records integrated with ITSM systems.
Without this step, vendors exit operational systems but remain in the risk surface: data they once held, access they were once granted, and obligations they were supposed to fulfill after termination all sit unmanaged.
Even organizations with a documented vendor risk management process tend to struggle with the same recurring gaps:
Manual workflows that don’t scale. Spreadsheets, email-based DDQs, and shared drives work for fifty vendors and collapse at five hundred.
Fragmented vendor inventories. Procurement, IT, and Legal each maintain their own lists that never fully reconcile.
Static, point-in-time assessments. Annual reviews catch a snapshot but miss everything that changes between reviews.
Disconnected contract and risk data. Contract terms live in one system; risk scores live in another; performance data lives in a third.
Limited 4th- and 5th-party visibility. Vendor’s vendors carry risk too, and most vendor risk management processes never look past the first hop.
No AI model governance. AI tools are entering the business through existing vendors faster than the vendor risk management process is being updated to govern them.
Audit scrambles. When a regulator or customer asks for evidence of a specific control, the response involves searching old emails rather than running a query.
These challenges are structural, not procedural. Fixing them requires connecting the stages of the vendor risk management process flow rather than running each one in a separate tool.
What Tools Are Used for Vendor Risk Management?
A mature vendor risk management process uses a layered set of tools, not a single one. The categories worth knowing:
Due-diligence questionnaires (DDQs). Structured assessments aligned to standards like SIG, CAIQ, ISO 27001, NIST SP 800-53, or HITRUST.
Sanctions and PEP screening tools. Automated checks against UN, EU, DFAT, OFAC, and other watchlists, with AML/CTF compliance verification built in.
Adverse media monitoring. AI-powered scanning across news sources and configurable feeds, with auto-classification into risk domains like data breaches, litigation, and financial events.
Cybersecurity ratings. Externally observable cyber-posture scores that surface technical risk without requiring a fresh assessment.
Financial health intelligence. Credit ratings, going-concern indicators, and financial-statement reviews.
Contract lifecycle management. AI-based extraction of SLAs, obligations, pricing, insurance terms, expiry, and renewal dates from executed contracts.
Performance management dashboards. SLA and KPI tracking with credits, earnbacks, and exception reporting.
Vendor portals. Self-service interfaces for vendor registration, document submission, performance self-reporting, and survey response.
Workflow automation. No-code workflow engines that handle intake, screening, DDQ dispatch, approvals, reminders, and escalations.
Reporting and analytics. Ad-hoc reporting, dashboards, and integration with BI tools like Tableau and Power BI.
The most capable approach unifies these categories on one platform. Running them on separate tools is what creates the fragmentation that breaks the vendor risk management process flow in the first place.
Best Practices for the Vendor Risk Management Process
Across regulated and non-regulated industries, the same best practices show up in mature programs:
1. Tier every vendor. Not all vendors deserve the same scrutiny. A risk-and-criticality tiering model ensures resources flow where they matter.
2. Move from point-in-time to continuous monitoring. Annual assessments cannot keep up with how fast vendor risk changes.
3. Look beyond cybersecurity. Financial, operational, reputational, ESG, geopolitical, and concentration risks are increasingly material.
4. Capture 4th and 5th parties. Your vendor’s vendors are your problem.
5. Embed risk into contracting. Build SLAs, audit rights, data-protection clauses, and termination triggers into every contract directly from assessment findings.
6. Automate the repeatable. Intake, screening, DDQ dispatch, reminders, scoring, and reporting are all automatable.
7. Govern the relationship, not just the onboarding. Most vendor risk tools stop after the contract is signed. Real risk emerges during the engagement.
8. Get cross-functional buy-in early. The vendor risk management process only works when InfoSec, procurement, legal, compliance, and the business agree on the operating model.
9. Maintain audit-ready records. Regulators don’t just want a process; they want documented evidence that it ran the way you said it did.
10. Plan the exit. Offboarding is a control, not an afterthought.
How to Evaluate Where Your Vendor Risk Management Process Stands
A few honest questions worth asking before assuming the vendor risk management process is in good shape:
Can you produce a current, risk-tiered list of your top 50 vendors in under an hour?
Is your vendor inventory the same across procurement, IT, legal, and compliance?
Are reassessments triggered by events, or only by the calendar?
Do you know which of your vendors use AI inside the products they sell you?
When a vendor appears in adverse news, how long does it take for that signal to reach the right internal stakeholder?
Can you trace, for audit, every step a specific vendor moved through in your vendor risk management process and what evidence was collected at each one?
If any of these answers cause hesitation, the vendor risk management process likely has structural gaps that no amount of additional manual effort will close.
Beyond the Process: Connecting Vendor Risk to Vendor Governance
A defined vendor risk management process solves the discipline problem: every vendor moves through the same stages, with documented evidence at each one. But the vendor risk management process flow doesn’t exist in isolation. It governs relationships with vendors whose contracts, performance, and AI usage all generate their own data, and managing those streams in separate systems creates exactly the kind of blind spots a vendor risk management process is supposed to eliminate.
Enlighta is a platform built to unify the full vendor risk management process on a single AI-powered foundation, from intake and screening through due diligence, contracting, onboarding, performance and compliance monitoring, governance, and offboarding. Unlike traditional vendor risk tools that stop at the contract, Enlighta governs the actual relationship: SLAs, KPIs, issues, obligations, adverse events, and 4th/5th-party concentration risk all live in the same record as the vendor’s risk score. AI-powered contract lifecycle management extracts SLAs, obligations, pricing, and insurance terms automatically rather than requiring manual review.
The platform’s approach to vendor governance was recognized in 2024 when Enlighta won the SIG Future of Sourcing Award for Innovation in Governance and Compliance alongside PepsiCo, for a partnership scaling supplier performance, governance, and contract compliance across regions and service categories.
For organizations whose AI tool exposure is growing faster than their vendor risk management process can keep up with, Enlighta’s GovernAI module brings vendor risk and AI model risk into one unified governance layer, so vendor governance and AI governance run on the same platform rather than as two disconnected programs.
Conclusion
The vendor risk management process is the discipline that turns vendor relationships from a hidden risk surface into a governed one. The steps themselves — identification, due diligence, contracting, onboarding, monitoring, governance, and offboarding — are well established. What separates mature programs from checkbox-driven ones is whether those steps are connected in a single workflow with documented evidence, or whether each one runs in its own tool and the gaps between them are where vendor failures originate.
If you’re evaluating where your vendor risk management process stands today, or how the stages of your vendor risk management process flow could work together in one platform, we’d be glad to walk you through it.
Frequently Asked Questions
What is an example of a vendor risk?
Common examples include a vendor experiencing a cybersecurity breach that exposes customer data, a supplier becoming insolvent, a vendor violating data-protection regulations like GDPR, a contractor caught in an ethical or labor-practices issue, or a supplier appearing on a sanctions list. Other examples include operational outages at a critical SaaS provider, concentration risk from over-reliance on a single vendor, and risks introduced through subcontractors that the primary organization never directly assessed.
What is the vendor risk management process?
The vendor risk management process is the structured sequence of activities used to identify, assess, mitigate, and continuously monitor risks introduced by vendors and service providers, from initial screening through to offboarding. It typically includes intake and tiering, due diligence and risk assessment, contracting, onboarding, ongoing monitoring, governance, and offboarding.
Why is the vendor risk management process important?
A structured vendor risk management process protects the organization from financial loss, regulatory penalties, operational disruption, and reputational damage caused by vendor failures. It also enables compliance with frameworks like DORA, GDPR, OCC guidance, and NYDFS Part 500, all of which hold the primary organization accountable for what its vendors do.
What are the key steps in the vendor risk management process?
The key steps are identification, screening, and tiering; due diligence and risk assessment; contracting and risk mitigation; onboarding and vendor information management; ongoing monitoring and performance management; governance and issue management; and offboarding and termination.
What are the common challenges in vendor risk management?
Common challenges include manual workflows that don’t scale, fragmented vendor inventories across procurement, IT, and legal, static point-in-time assessments that miss real-time risk changes, disconnected contract and risk data, limited visibility into 4th and 5th parties, lack of AI model governance, and audit-readiness gaps that surface only when a regulator asks.
What tools are used for vendor risk management?
Mature programs use a layered toolset: due-diligence questionnaires, sanctions and PEP screening, adverse media monitoring, cybersecurity ratings, financial health intelligence, contract lifecycle management with AI extraction, performance dashboards, self-service vendor portals, workflow automation, and reporting and analytics. The most effective approach unifies these on one platform rather than running them as separate tools.
What is the vendor risk management process flow?
The vendor risk management process flow is the visible sequence each vendor moves through: intake, screening, tiering, due diligence, contracting, onboarding, ongoing monitoring, governance and issue management, and offboarding. A well-defined flow ensures every vendor is governed consistently, with documented evidence collected at each stage.
Explore the full program: this guide is part of the Supplier Risk Management hub — the complete lifecycle, risk categories, KPIs and free templates in one place.
Tag:
Share Article:
Enlighta Team
Enlighta’s software solutions empower enterprises to increase business value and mitigate risks in supplier and third-party engagements through data-driven insights into demand, performance, contract compliance & spend, and process automation for demand, selection, invoice validation, vendor governance, and third-party risk monitoring.